What Your AWS Architecture Diagram Isn't Telling You | Savishty
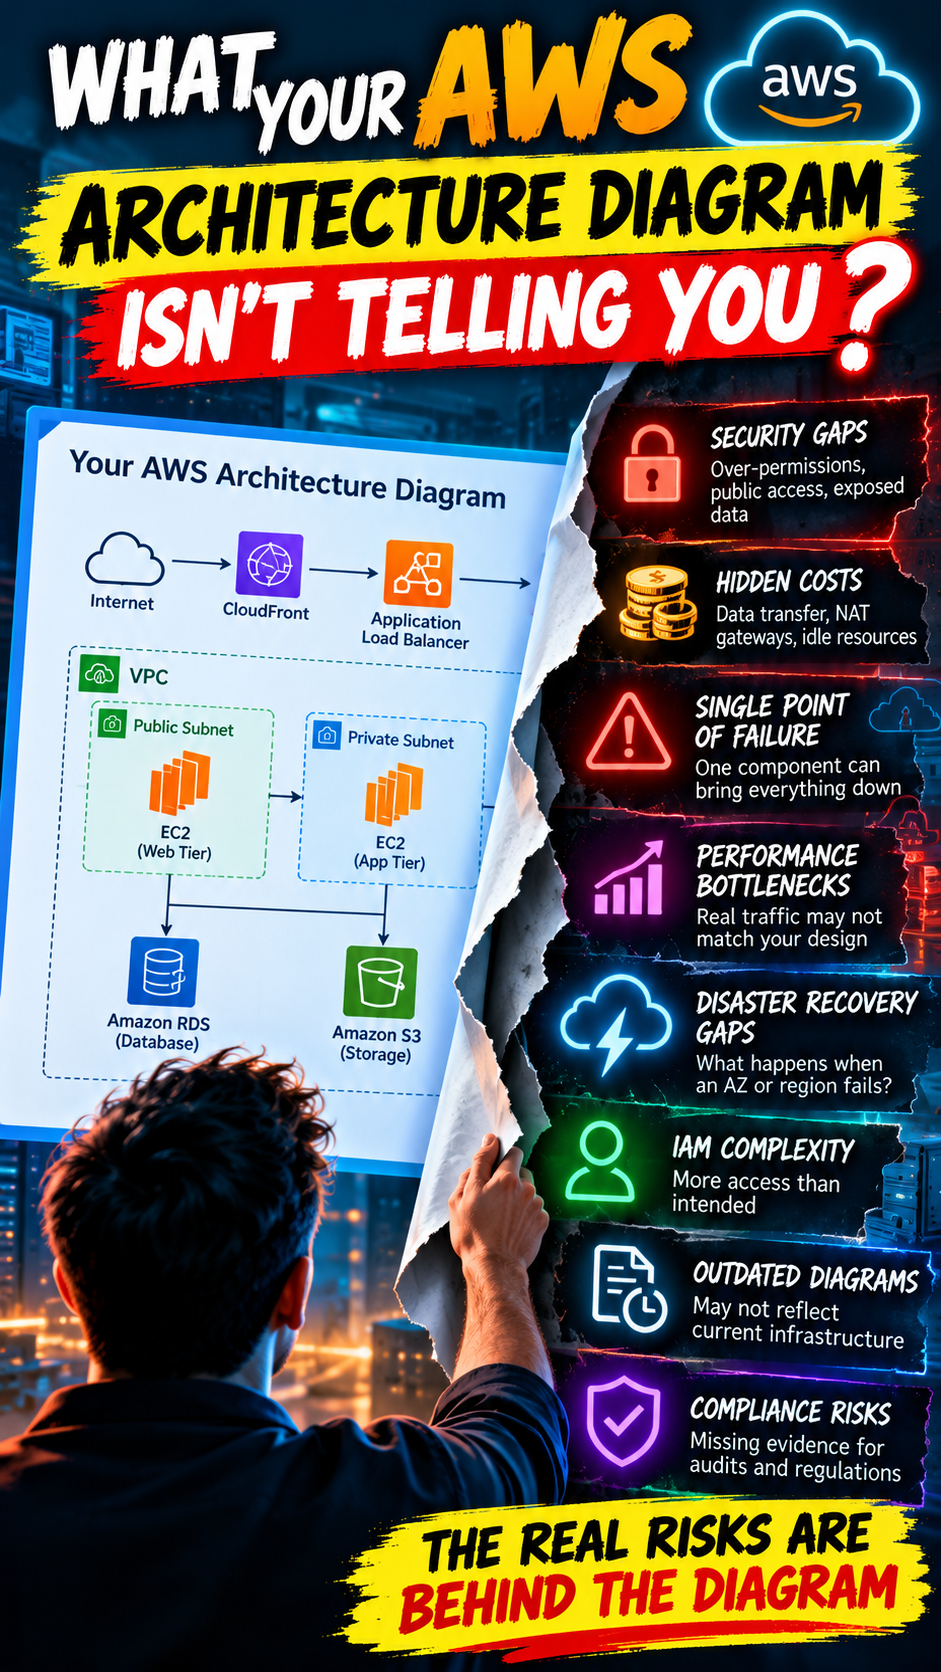
Your AWS architecture diagram looks perfect. Every service is connected, every component has a place, and the entire system appears ready for production. But what if the biggest risks in your cloud infrastructure are the things your diagram doesn't show?
An AWS architecture diagram is supposed to make complex cloud environments easier to understand. It illustrates how applications, databases, networking components, security services, and other resources interact. For architects, developers, DevOps engineers, and business leaders, it provides a visual overview of how a system is designed.
But there is a problem: a clean architecture diagram does not necessarily mean a secure, reliable, or cost-efficient cloud environment.
Behind those neat boxes and connecting lines could be excessive permissions, hidden network dependencies, expensive data transfers, weak disaster recovery plans, and bottlenecks that only appear when real users arrive.
Let's explore what your AWS architecture diagram might be hiding — and why these invisible details matter more than ever.
1. Your Diagram Shows Connections, Not Security Risks
Security Groups vs ACLs Explained
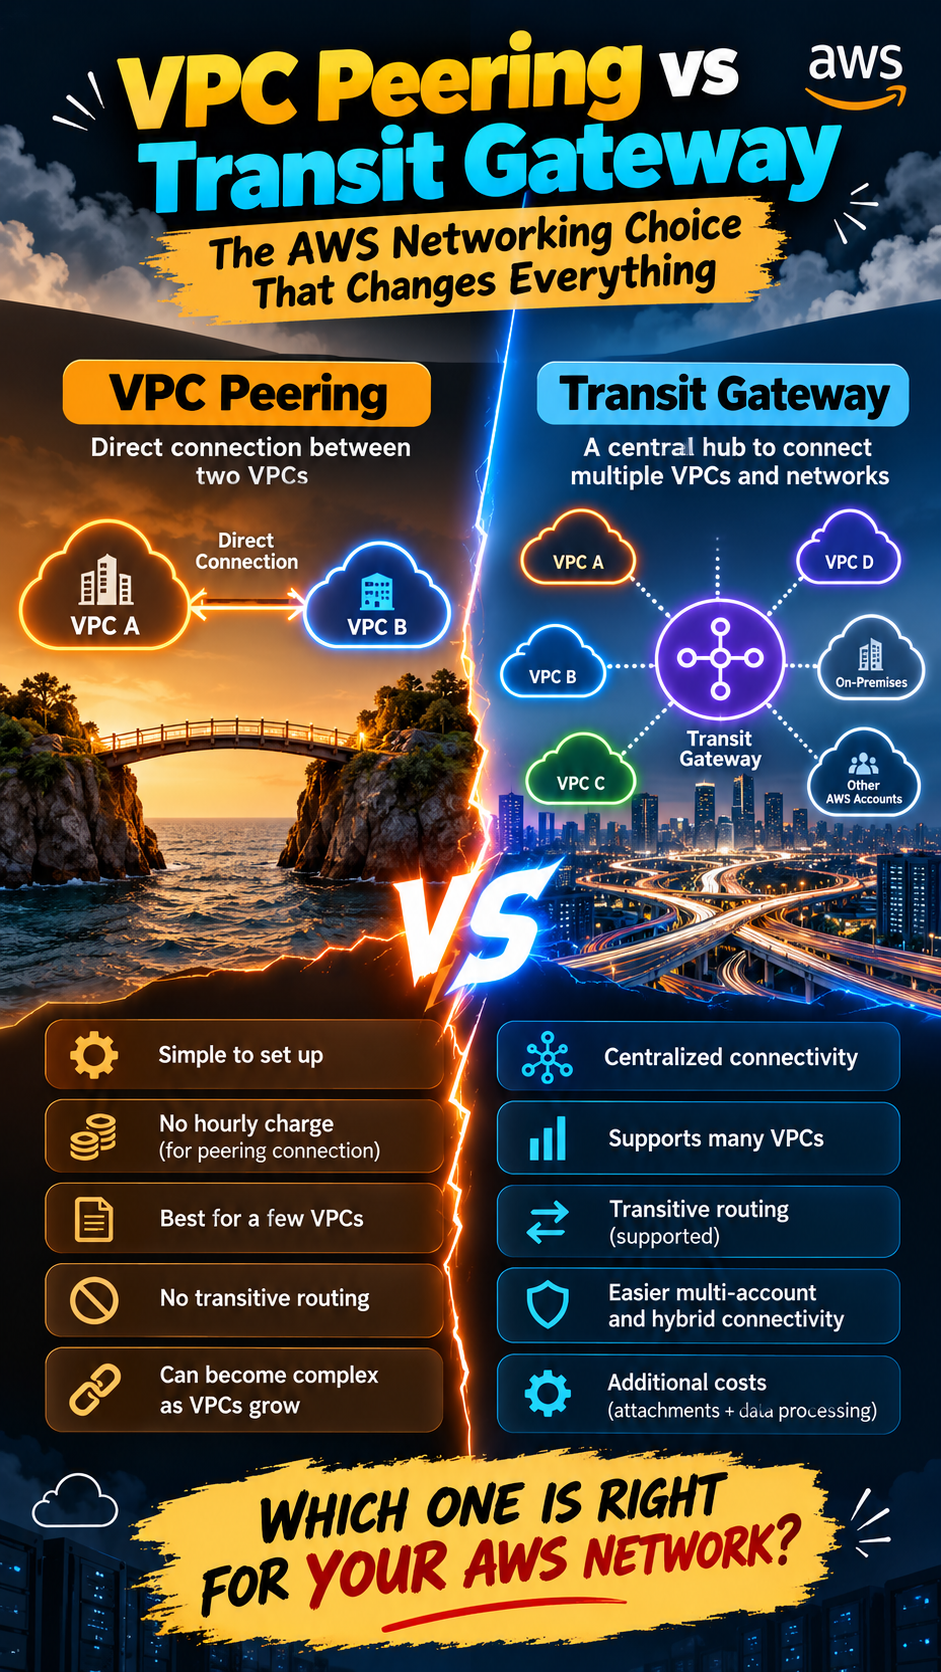
Most architecture diagrams show how services connect. They rarely communicate whether those connections are secure.
For example, a diagram might show an application server connecting to an Amazon RDS database. Everything looks normal. But the diagram may not reveal that the database is publicly accessible, security group rules allow unnecessary inbound traffic, or the application has excessive IAM permissions.
These problems can create security vulnerabilities even when the architecture appears well designed.
What your diagram might be missing
Whether Amazon S3 buckets expose sensitive data.
Whether IAM roles follow the principle of least privilege.
Whether security groups permit unnecessary network access.
Whether secrets are stored securely or embedded in application configurations.
Whether sensitive data is encrypted in transit and at rest.
The reality: A connection between two services tells you that communication is possible. It does not tell you whether that communication is appropriately restricted.
To close this visibility gap, combine architecture diagrams with AWS IAM Access Analyzer, AWS Config, security group reviews, and other appropriate security assessment tools.
2. Your Architecture Might Be More Expensive Than You Think
A cloud architecture can look efficient on paper and still generate surprisingly high AWS bills.
Why? Because architecture diagrams typically show which services exist, not how much those services cost to operate.
Consider an application deployed across multiple Availability Zones. The design may improve resilience, but cross-AZ data transfer, load balancers, NAT gateways, logging, and storage requests can add substantial costs depending on workload behavior and configuration.
Similarly, an architecture with frequent communication between regions can generate data transfer charges that are difficult to spot in a high-level diagram.
Hidden cost drivers to investigate
Architecture component
Potential hidden cost
NAT gateways
Processing charges and associated data transfer
Cross-AZ traffic
Data transfer charges for applicable traffic
Multi-region deployments
Inter-region transfer, replication, and duplicated resources
CloudWatch logging
Log ingestion, storage, and query costs
Overprovisioned compute
Paying for more capacity than workloads need
Data storage and backups
Growing retention, snapshot, and replication costs
The answer is not to remove every expensive service. A NAT gateway, multi-AZ database, or cross-region replica may be essential for the business.
Instead, the goal is to understand the trade-off between cost, availability, performance, and security.
A better architecture diagram should be supported by cost estimates, traffic assumptions, and ongoing AWS billing analysis.
3. Your Diagram Doesn't Reveal What Happens During a Failure
Designing a Multi-Region Disaster Recovery Architecture on AWS | by Archita | Medium
Many AWS diagrams show a healthy application running across multiple Availability Zones. Some even show a backup region.
But here is the important question: What happens when something actually fails?
A diagram might include a standby database without explaining how failover occurs, how quickly the application recovers, or whether the standby environment has enough capacity to handle production traffic.
Likewise, having backups does not automatically mean your application can recover within an acceptable timeframe.
Ask these questions about your architecture
What happens if an Availability Zone becomes unavailable?
Can the application continue if its primary database fails?
Are backups isolated from accidental deletion or compromised credentials?
Has the disaster recovery process been tested?
What are the required Recovery Time Objective (RTO) and Recovery Point Objective (RPO)?
Are critical dependencies available during a regional outage?
A highly available architecture and a disaster recovery strategy are related, but they are not interchangeable.
A robust AWS design documents failure scenarios, recovery procedures, dependency requirements, and the time needed to restore business operations.
4. Your Diagram May Hide a Single Point of Failure
Building Reliable Infrastructure in Google Cloud | by Sumit K | Google Cloud - Community | Medium
A system can contain dozens of AWS services and still depend on one component that brings everything down when it fails.
This is known as a single point of failure.
Imagine an application deployed across several Availability Zones but dependent on one critical external API, a single-instance processing service, or a centralized component without adequate redundancy.
The application may appear distributed, yet one dependency can disrupt the entire user experience.
Other potential weak points include:
A single NAT gateway serving multiple private subnets without a suitable resilience strategy.
A queue consumer that cannot scale during traffic spikes.
A centralized authentication service with no tested recovery approach.
A database configuration that cannot meet the required availability target.
A deployment pipeline that becomes a bottleneck during emergency recovery.
The key is to examine the entire dependency chain rather than count the number of servers or services.
Resilience comes from eliminating or managing critical failure points — not simply adding more cloud resources.
5. Your Diagram Doesn't Show Real Traffic Behavior
Architecture diagrams usually represent systems as static structures. Real applications, however, behave differently under changing workloads.
A design may perform perfectly with 100 concurrent users and struggle with 10,000. A database may handle normal queries comfortably but become overloaded during reporting jobs or sudden traffic spikes.
Without traffic patterns and performance assumptions, the diagram tells only part of the story.
What might be missing?
Expected concurrent users and request volumes.
Peak traffic and seasonal demand.
Database connection limits and query bottlenecks.
Queue backlogs and processing delays.
Auto Scaling policies and scaling delays.
Rate limits imposed by third-party services.
Latency between regions, services, and data stores.
For example, adding more EC2 instances may not improve performance if the real bottleneck is a database that cannot handle additional connections.
To understand these issues, combine architectural reviews with load testing, application metrics, distributed tracing, and performance monitoring.
Useful tools include Amazon CloudWatch, AWS X-Ray, and AWS Application Signals where applicable.
6. Your Diagram May Ignore IAM Complexity
Security architecture is more than drawing a lock icon next to a service.
In AWS, identities and permissions determine which users, applications, and services can access resources. These permissions may be distributed across IAM roles, resource policies, trust policies, permission boundaries, and service-specific controls.
A diagram that shows an application accessing S3 does not necessarily explain whether it can read one bucket or access hundreds of unrelated resources.
Similarly, an EC2 instance may need access to one S3 bucket but have permissions extending far beyond that requirement.
Questions worth investigating
Are workloads using IAM roles instead of unnecessary long-lived access keys?
Are permissions limited to required actions and resources?
Are cross-account roles and trust relationships reviewed?
Are sensitive operations logged and monitored?
Can compromised application credentials access unrelated services?
Use IAM Access Analyzer, AWS CloudTrail, and appropriate policy reviews to assess the real permissions behind the visual design.
An architecture diagram should help explain the security model, but it should never be treated as proof that the model is secure.
7. Your Diagram Might Be Outdated
The Real Reason Architecture Diagrams Go Stale - DEV Community
This is one of the most overlooked problems in cloud environments.
A diagram created six months ago may no longer reflect the infrastructure running today.
Perhaps a developer introduced a new service, a team migrated a database, or an emergency change opened a network path that never made it into the documentation.
Over time, the diagram and the actual environment begin to diverge.
This creates several risks:
Engineers troubleshoot the wrong dependencies.
Security reviews overlook undocumented resources.
Incident response teams lose valuable time.
New employees misunderstand the deployment.
Cloud migrations become harder to plan accurately.
To prevent this, establish clear ownership of architecture documentation and update it when meaningful infrastructure changes occur.
Where possible, use infrastructure-as-code repositories, automated discovery, and configuration inventory tools to compare the intended design with deployed resources.
Tools such as AWS Config and AWS Resource Explorer can help teams inspect resources and configurations, although neither automatically guarantees a complete, accurate architecture diagram.
8. Your Architecture May Not Be Ready for Compliance Audits
A diagram can show encryption, network isolation, and access controls without demonstrating that these controls are correctly configured or consistently enforced.
This distinction matters for organizations working with sensitive information or operating under regulatory and contractual requirements.
For example, an architecture diagram may indicate that data is encrypted, but it might not document key-management responsibilities, retention policies, access reviews, or evidence that controls operate as intended.
Depending on the applicable requirements, teams may need to assess:
Data classification and data flow.
Encryption and key-management configuration.
Identity and access controls.
Audit logging and retention.
Backup protection and recovery testing.
Network segmentation and security monitoring.
AWS services such as AWS Config, AWS CloudTrail, AWS Security Hub, and AWS Audit Manager may support parts of this process, depending on service availability, configuration, and the compliance framework involved.
Documentation communicates the intended control; technical evidence helps demonstrate whether the control is actually working.
9. How to Make Your AWS Architecture Diagram More Useful
You do not need to replace your existing diagram with a complicated technical blueprint. You need to supplement it with the information required to make good engineering decisions.
Here is a practical review checklist.
AWS Architecture Review Checklist
0 of 6
Security
Review IAM permissions, security groups, encryption, secrets, and public exposure.
Cost
Identify NAT gateway usage, data transfer paths, storage growth, and oversized resources.
Resilience
Document failure scenarios, dependencies, backups, RTO, and RPO.
Performance
Record traffic assumptions, scaling behavior, database limits, and bottlenecks.
Accuracy
Compare documentation against deployed resources and infrastructure-as-code.
Operations
Document monitoring, alerting, ownership, deployment, and recovery procedures.
Copy review checklist
Conclusion: The Real Architecture Is More Than What You Can See
Your AWS architecture diagram is an important starting point, but it is not the complete picture.
It may show where services run without revealing whether they are secure. It may illustrate redundancy without proving that failover works. It may display a scalable design without showing where performance bottlenecks will appear. And it may look perfectly accurate while the actual infrastructure has already changed.
The solution is to treat architecture diagrams as living engineering documents and pair them with security assessments, cost analysis, performance testing, configuration reviews, and disaster recovery exercises.
Ultimately, a well-designed AWS environment is not one that simply looks good on a diagram. It is one that remains secure under attack, stable during failures, efficient under load, and financially sustainable as it grows.
Because the most expensive cloud problems are often the ones your architecture diagram never warned you about.
Did you find this helpful?