Your CI/CD Pipeline Has More Power Than You Think | Savishty
Your CI/CD Pipeline Has More Power Than You Think
Your CI/CD pipeline isn't just deploying code. It could be the most powerful—and most overlooked—attack path in your entire cloud infrastructure.
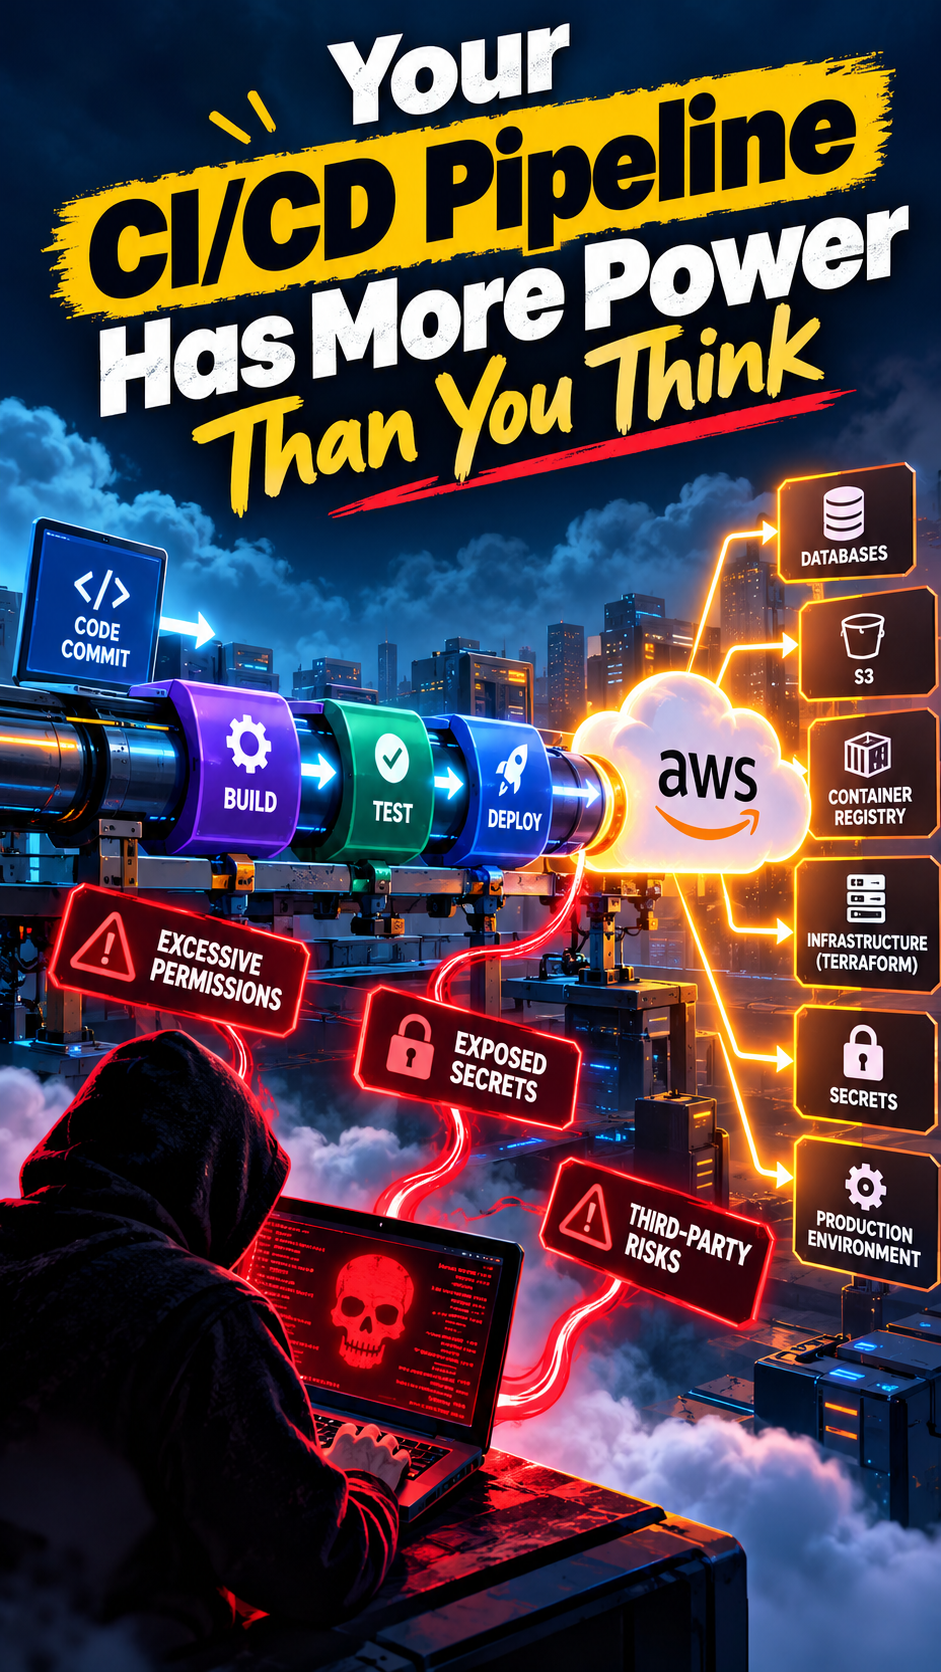
Imagine this: A developer pushes a small code change to GitHub. Within seconds, your CI/CD pipeline kicks in, runs automated tests, builds a Docker image, and deploys the application to AWS.
Everything works perfectly.
But behind the scenes, that same pipeline might have access to production databases, AWS credentials, container registries, and infrastructure management tools. If an attacker compromises it, they may gain access to far more than your source code.
And here's the scary part: your pipeline might already have more permissions than it actually needs.
Let's explore why CI/CD security matters, how pipelines become a major security risk, and what you can do to protect your cloud environment.
What Makes CI/CD Pipelines So Powerful?
Continuous Integration and Continuous Deployment (CI/CD) pipelines automate the process of testing, building, and deploying software.
Tools such as GitHub Actions, GitLab CI/CD, Jenkins, and AWS CodePipeline help teams release software faster with fewer manual steps.
But automation requires access.
Depending on how your pipeline is configured, it might have permission to:
Read and modify source code repositories.
Access AWS services and cloud resources.
Build and publish Docker images.
Deploy applications to production.
Update infrastructure using Terraform.
Retrieve secrets from environment variables or secret managers.
Execute scripts and third-party tools during builds.
In other words, a CI/CD pipeline can act as a trusted operator inside your infrastructure.
If an attacker compromises a developer's laptop, the damage may be limited by that user's permissions. But if the attacker compromises a pipeline with administrator-level cloud access, the potential impact can be significantly greater.
The real risk isn't automation itself. It's giving automation too much trust.
1. The Hidden Danger of Overprivileged IAM Roles
One of the most common cloud security mistakes is assigning excessive permissions to CI/CD pipelines.
For example, a deployment workflow might use an AWS IAM role with the AdministratorAccess policy because it was convenient during initial setup.
The application deploys successfully, so nobody revisits the configuration.
Months later, the same role still has broad access to services that the pipeline never needs.
Consider a workflow that only needs to upload application files to a specific Amazon S3 bucket. Does it really need permission to modify IAM policies, delete databases, or create new users?
Probably not.
If an attacker gains control of that workflow, excessive permissions could allow them to perform actions far beyond the original deployment task.
How to reduce the risk
Apply the principle of least privilege.
Create dedicated IAM roles for individual applications and environments.
Grant only the specific actions required for deployment.
Restrict access to the necessary AWS resources.
Separate development, staging, and production permissions.
Review IAM policies regularly.
Avoid using administrator credentials in automated workflows.
For example, a frontend deployment role should not automatically receive permission to modify production databases or IAM users.
Security rule: If your pipeline doesn't need a permission, don't give it that permission.
2. Your Secrets Could Be Exposed in the Pipeline
CI/CD pipelines frequently handle sensitive information, including API tokens, database credentials, private keys, and cloud access credentials.
These secrets may be stored in repository settings, environment variables, configuration files, or external secret managers.
The danger appears when workflows expose them accidentally.
A developer might enable verbose logging to troubleshoot a failed build. A script might print environment variables. A third-party action might receive access to secrets it doesn't need.
In the worst case, a compromised workflow could send credentials to an external server.
Once an attacker obtains valid credentials, they may be able to access cloud resources without exploiting a traditional software vulnerability.
How to protect your secrets
Never commit credentials to source control.
Use AWS Secrets Manager or AWS Systems Manager Parameter Store where appropriate.
Prefer short-lived credentials over long-lived access keys.
Mask sensitive values in logs, while remembering that masking is not a complete security boundary.
Restrict which workflows and jobs can access secrets.
Rotate credentials if exposure is suspected.
Avoid passing secrets to untrusted third-party actions.
For AWS workloads, consider using temporary credentials through IAM roles rather than storing permanent AWS access keys in CI/CD variables.
The fewer long-lived secrets your pipeline contains, the fewer opportunities attackers have to steal them.
3. A Compromised Pipeline Can Become a Production Backdoor
Think about your deployment process.
Your pipeline retrieves code, installs dependencies, builds an artifact, and deploys it to production.
Now imagine an attacker modifies a workflow file or compromises a dependency used during the build.
The pipeline may execute malicious code using the same permissions it normally uses for legitimate deployment.
That code could attempt to steal secrets, modify build artifacts, or introduce malicious functionality into an application.
Because the deployment comes through an authorized automation process, the activity may initially appear legitimate.
This is why protecting the production environment alone isn't enough. You must also protect the systems that are authorized to change it.
Security measures that help
Protect production branches with mandatory reviews.
Require approval before production deployments.
Restrict who can modify workflow files.
Pin third-party CI/CD actions to verified commit SHAs where supported.
Scan dependencies and build artifacts.
Generate and verify software provenance and artifact attestations where practical.
Separate build and deployment permissions.
Monitor unexpected changes to production resources.
A successful security strategy doesn't simply ask, "Who can access production?"
It also asks, "Who—or what—can deploy code into production?"
4. Terraform Automation Can Increase the Blast Radius
Infrastructure as Code makes cloud infrastructure repeatable and easier to manage. Tools such as Terraform allow teams to create and update AWS resources through automated workflows.
However, Terraform pipelines can be particularly sensitive because they may modify the infrastructure that protects your entire environment.
Imagine a Terraform deployment role that can change security groups, modify IAM roles, delete resources, and update networking configurations.
If the pipeline is compromised, an attacker may attempt to weaken security controls, create unauthorized access paths, or disrupt production infrastructure.
The problem becomes more serious when the pipeline also has access to Terraform state files containing sensitive infrastructure information.
Recommended safeguards
Restrict access to Terraform state and state-locking resources.
Encrypt remote state and tightly control who can read it.
Require plan reviews before sensitive production changes.
Apply appropriate approval gates before
terraform apply.Use separate roles and state backends for different environments when appropriate.
Monitor unexpected infrastructure changes.
Keep state backups and test recovery procedures.
Remember: a Terraform pipeline doesn't just deploy applications. Depending on its permissions, it may be able to change the architecture and security posture of your entire cloud environment.
5. Third-Party CI/CD Actions Can Introduce Supply Chain Risk
Modern pipelines often rely on reusable actions, plugins, packages, and external scripts.
They save development time, but each additional dependency introduces a potential trust decision.
What happens if a third-party action is compromised? What if a dependency update introduces malicious code? What if a workflow downloads and executes a script from an external location without verifying its integrity?
If that code runs inside a privileged pipeline, it may inherit access to credentials, source code, or cloud resources.
Reduce your supply chain exposure
Use trusted and maintained actions.
Pin actions and dependencies to known versions or immutable identifiers where possible.
Review permission requirements before adding new integrations.
Avoid executing unverified remote scripts in privileged jobs.
Use dependency scanning and software composition analysis.
Keep build environments isolated.
Review changes to workflow dependencies as carefully as application code.
Third-party automation should be treated like production software—not harmless configuration.
6. A Successful Deployment Doesn't Mean a Secure Deployment
Most CI/CD pipelines focus on delivery metrics:
Did the build pass?
Did the tests succeed?
Was the application deployed?
Did the deployment finish on time?
These are important questions, but they don't tell you whether the pipeline followed secure practices.
A deployment can succeed even when a workflow uses excessive permissions, exposes credentials, or downloads untrusted dependencies.
Security must become part of the delivery process itself.
Consider adding automated checks for:
Exposed secrets.
Vulnerable dependencies.
Container image vulnerabilities.
Insecure infrastructure configurations.
Unexpected IAM permission changes.
Unapproved production deployments.
Suspicious workflow modifications.
The goal is not to slow down every release. It's to catch dangerous changes before they reach production.
7. How to Secure Your CI/CD Pipeline on AWS
If your organization deploys applications to AWS, use this practical checklist as a starting point.
Security areaRecommended actionIAM permissionsApply least privilege to every pipeline role.AuthenticationPrefer temporary credentials and workload identity federation where supported.SecretsStore secrets securely and limit access by job and environment.Git securityProtect branches and require reviews for sensitive changes.Production accessRequire appropriate approvals for high-risk deployments.DependenciesPin and verify third-party actions and build dependencies.TerraformProtect state files and review infrastructure plans.MonitoringAudit cloud API activity and investigate unexpected changes.RecoveryTest credential revocation and pipeline recovery procedures.
A practical AWS example
Suppose GitHub Actions deploys an application to Amazon ECS.
Instead of storing permanent AWS access keys in GitHub secrets, configure an IAM role that GitHub Actions can assume using OpenID Connect (OIDC).
Then:
Restrict the role's trust policy to the expected GitHub organization, repository, and deployment context.
Grant the role only the permissions required for the intended deployment.
Separate development and production roles.
Require appropriate approval before production deployment.
Log and monitor relevant AWS API activity.
Test whether a compromised workflow could access unrelated resources.
OIDC reduces reliance on long-lived AWS credentials, but it does not automatically make a pipeline secure. Trust policies, role permissions, workflow protections, and secret handling still matter.
The Bottom Line: Your Pipeline Is Part of Your Security Perimeter
CI/CD pipelines have become essential to modern software delivery. They help teams ship features faster, reduce manual effort, and manage complex cloud environments.
But their power comes with responsibility.
A pipeline with broad cloud permissions, exposed credentials, and unrestricted deployment access can become a high-impact attack path.
The solution isn't to stop automating. It's to make automation secure by design.
Start by auditing your IAM roles, removing unnecessary permissions, eliminating long-lived credentials where possible, protecting workflow changes, and monitoring deployment activity.
Then ask your team one critical question:
If someone compromised our CI/CD pipeline today, how much of our cloud infrastructure could they control?
If you don't know the answer, it's time to find out—before an attacker does.
Did you find this helpful?